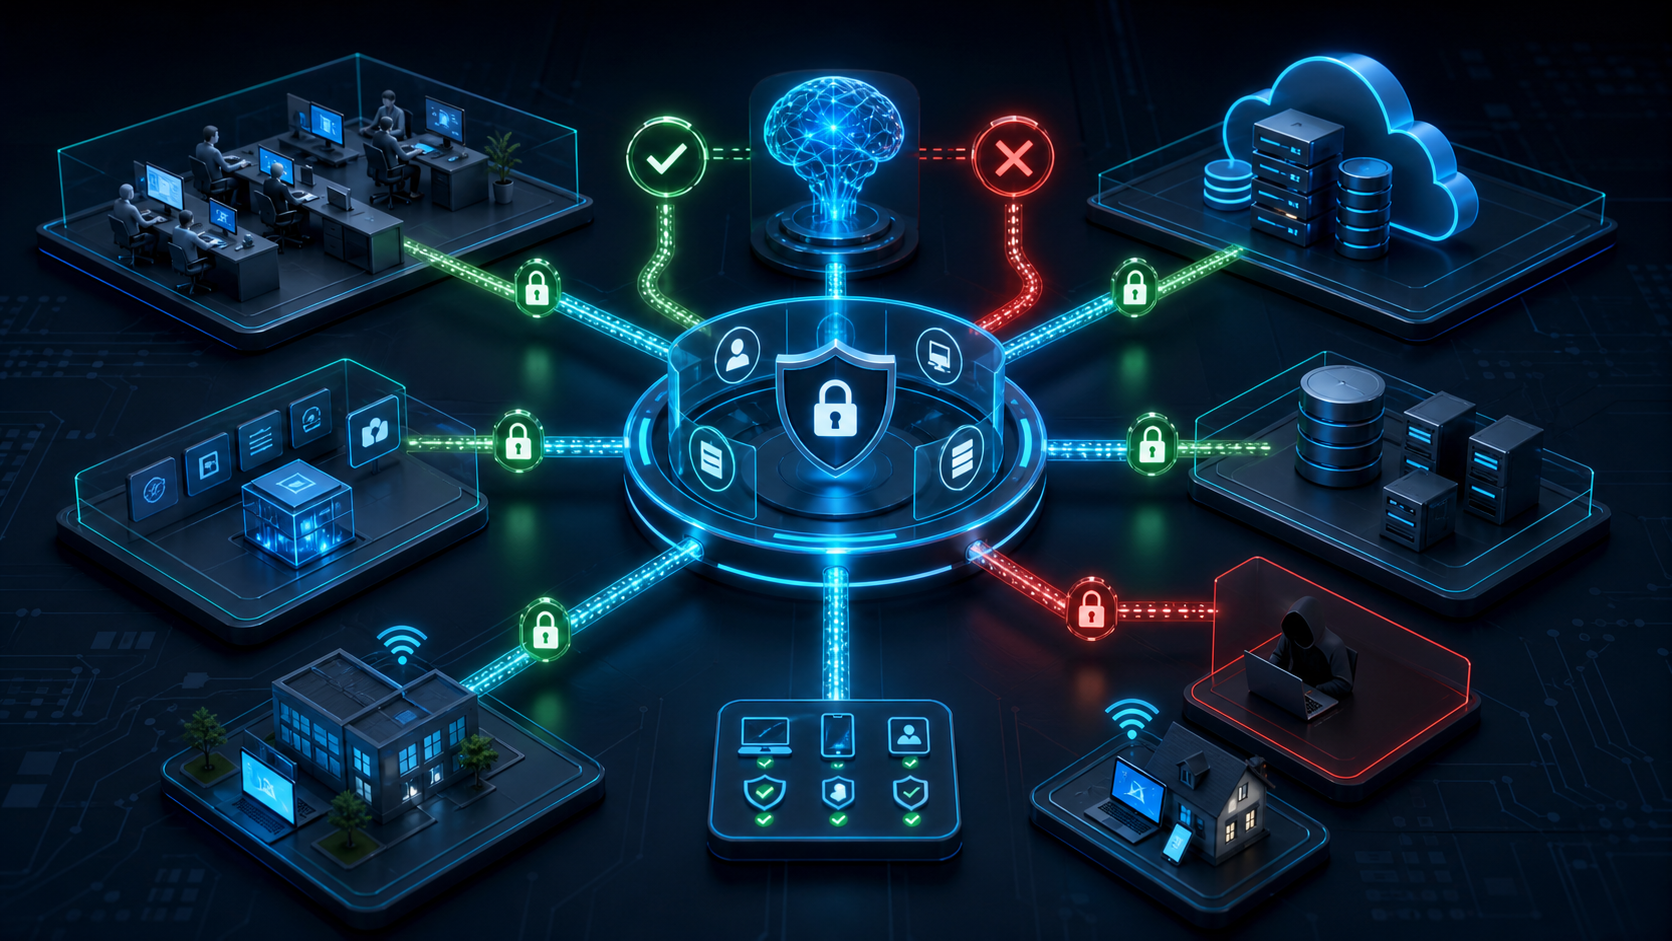
Zero Trust network design removes the assumption that a request is safe merely because it originates inside a network. The practical task is to decide which identity can reach which resource, under what conditions, and where that decision is enforced.
My campus, access-network and IAM labs provide examples for thinking through these boundaries. They demonstrate individual concepts, not a complete enterprise Zero Trust deployment or a certified implementation.
Start with resources and access requirements
List the applications, administration paths and data flows that matter. Identify the users, service identities and devices that need each path. A network diagram alone rarely explains why an access rule exists.
For a first review, select one application and describe its required connections. Include supporting services such as DNS, identity and monitoring. Ask what the application should do if one of those dependencies is unavailable.
Combine segmentation with identity checks
Separate guest access, user traffic, service workloads and management where the design requires it. A VLAN separates broadcast domains; it does not by itself establish identity-aware authorization between resources.
Identity controls can evaluate who is requesting access. Network controls constrain the permitted path. Application permissions still govern what the user can do after a connection is established. Each layer needs an owner and a testable purpose.
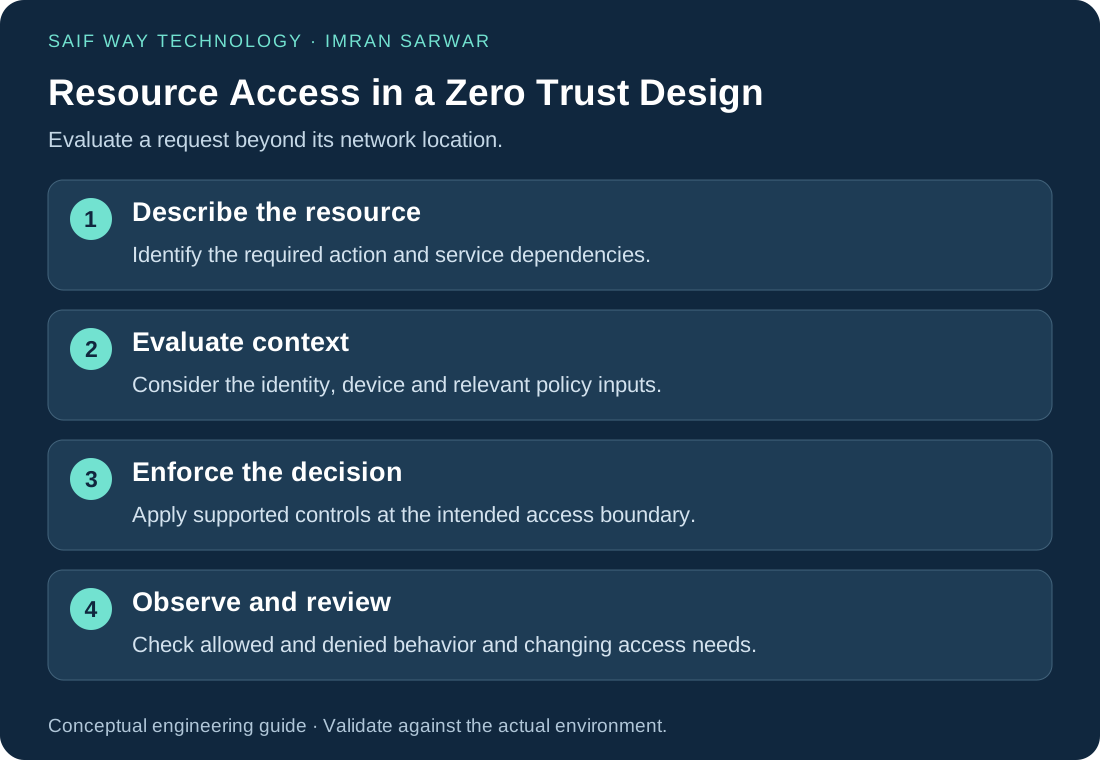
Make policy enforceable and observable
Translate the requirement into rules at supported enforcement points. Check the allowed action, destination and context, then record how a denied request appears in the evidence available to operations.
NIST’s Zero Trust Architecture publication describes the resource-focused approach. For implementation guidance, the UK NCSC’s ZTNA guidance is a useful reference. Neither reference proves that a particular lab meets every architectural requirement.
Test access approval, use and revocation
Use an approved test identity and exercise the required operation. Then test a denied identity or invalid context and confirm the observed outcome. Check what happens when permissions change or a relevant service fails.
Avoid opening broad access simply to make a test pass. Investigate the missing dependency and decide whether it is part of the legitimate requirement. Document the resulting exception and who will review it.
Translate Zero Trust policies into support procedures
The campus network project provides network context, while IDMUI shows identity-related application work. Read the IAM access-review article for role scope and lifecycle questions.
If your current issue is connectivity or an implementation boundary, describe the systems, required access and failure evidence through remote infrastructure support. A scoped technical review establishes what can be assessed; this article does not promise a full Zero Trust transformation service.