A network security architecture review connects requirements with controls that can be implemented and operated together. Listing Zero Trust, defense in depth, monitoring and recovery is not yet a design: the team must explain where each control acts and how it will be tested.
This article develops my security-design learning, including study of Cisco security infrastructure design concepts. It is not an official Cisco guide or a claim of a new certification. The portfolio links show related labs and applications; the discussion below is a review method.
Start with a concrete access scenario
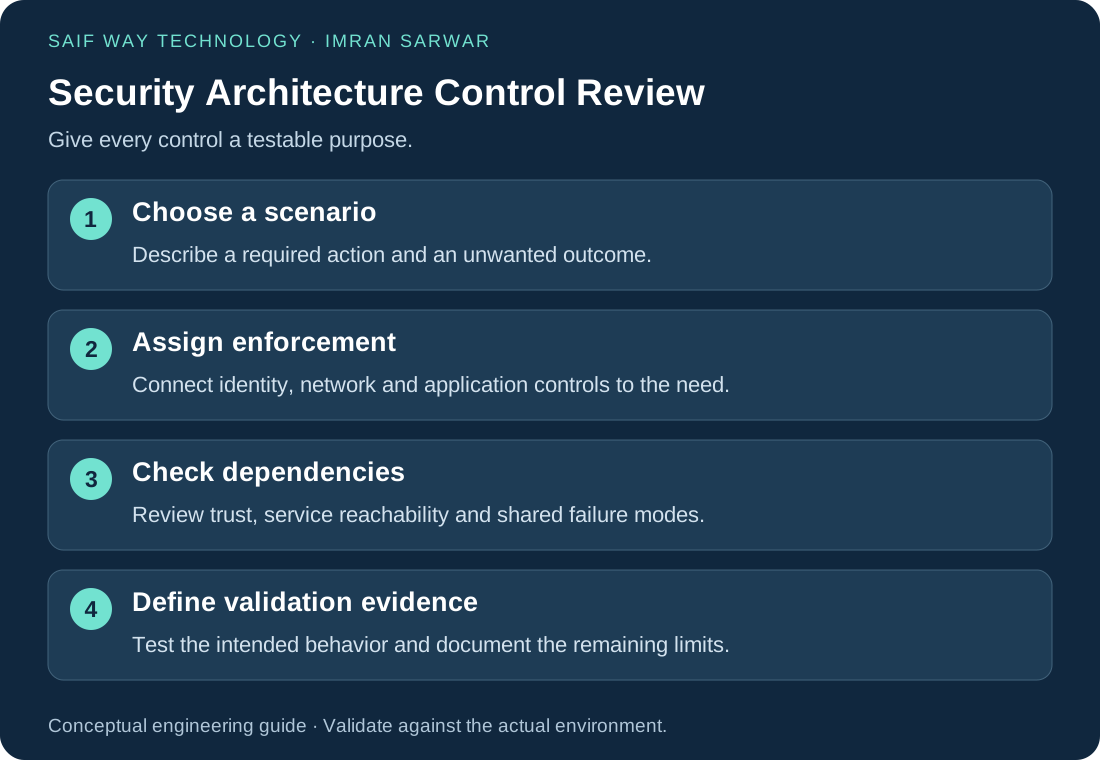
Choose a workflow such as an administrator changing a network device or an application requesting a certificate. Identify the actor, target, required action, data and dependencies. Define an unwanted action that the design should prevent or reveal.
A narrow scenario makes control selection more useful. It also exposes assumptions that broad labels hide: where authentication happens, whether a management connection crosses a trust boundary and which system records the outcome.
Define the security purpose of each infrastructure layer
An identity control can restrict who requests an action. A network rule can constrain the path. Application authorization can govern the action on the target resource. Telemetry can make the result reviewable. Recovery arrangements limit the impact if the change fails.
Defense in depth is strongest when the layers address the scenario and their shared dependencies are understood. Several controls that all depend on one unavailable identity or management service may share a failure mode.
Review policy interactions and access exceptions
Check certificate trust, DNS, time synchronization, token handling and service reachability where the workflow depends on them. An access failure can result from a dependency rather than the primary policy.
Describe how an exception is approved, constrained and reviewed. Avoid an emergency workaround becoming a permanent broad rule. Operators need to understand why a control exists and how to investigate a denied request.
Define evidence before testing
For each requirement, write the expected allowed and denied behavior and the observation that supports it. A successful login does not establish correct authorization. A configuration line does not prove that traffic is being evaluated at the intended boundary.
NIST’s Zero Trust reference provides a framework for resource access. Use the deployment checklist for release evidence and resilience testing for failure scenarios. These articles serve different review stages rather than repeating a single security checklist.
Translate the security-design review into implementation tasks
The IDMUI project provides identity/application context. The certificate-management project provides lifecycle context, while the campus lab shows network design learning.
For an existing infrastructure or Python application, prepare the workflow, boundary, error and expected outcome. A technical scope discussion can establish whether a targeted review or implementation task fits my documented experience. It does not assume a full enterprise security-assurance engagement.