Identity and access management (IAM) answers who can perform an action and under what scope. In cloud infrastructure, an overly broad assignment can expose resources even when network connectivity is well controlled.
My OpenStack Keystone and IDMUI work helped me connect users, roles, projects and tokens with day-to-day administrative decisions. This article focuses on reviewing access. It complements the separate Flask application walkthrough rather than repeating its UI architecture.
Separate identity, permission and scope
Authentication establishes an identity. Authorization evaluates an action against policy. A role name alone is not enough to describe effective access: its scope and the service’s configured policy also matter.
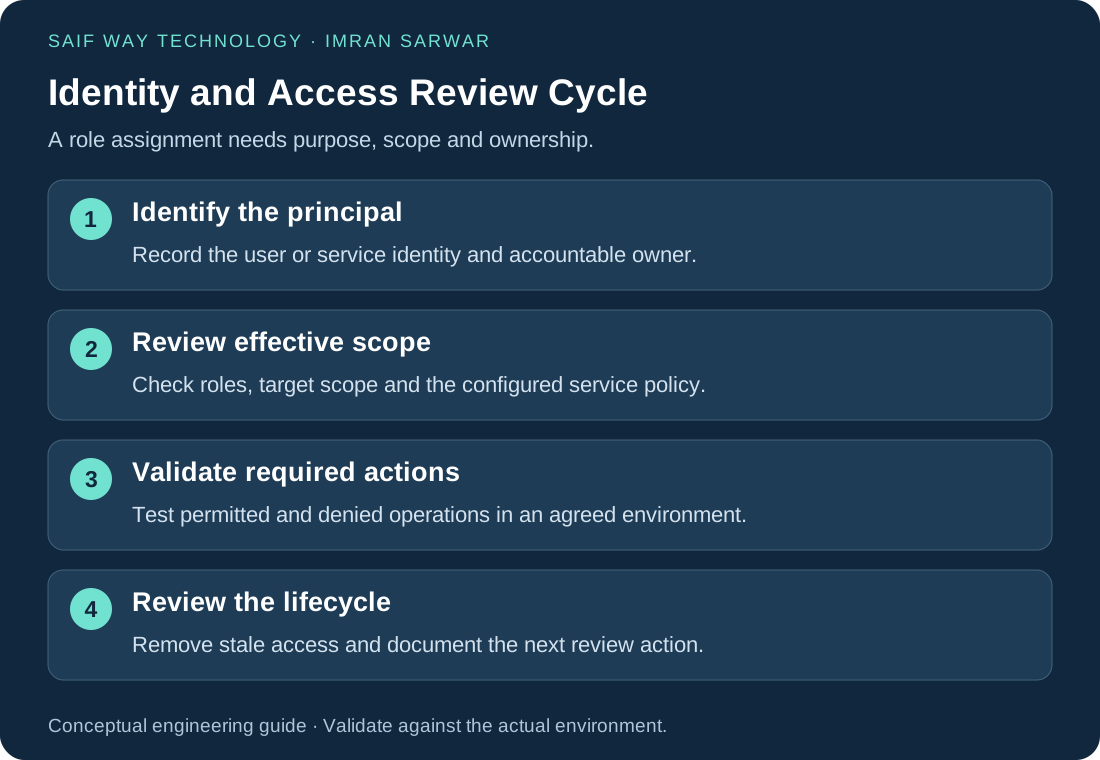
For a review, list the principal, assigned role, target scope, business purpose and owner. Ask whether the access is still required and how it will be removed. Shared accounts make that ownership harder to establish.
Review administrative access separately
A user who needs a read operation may not need account creation or role assignment rights. A service integration should have the permissions required for its task, not simply reuse an administrator’s identity.
Check both successful and denied operations in a test environment. The Keystone role documentation describes how default roles interact with scope; verify your deployment’s release and policy before applying those expectations.
Example IAM access-review record
Suppose an integration needs a limited operation in one project. Review the requested permission, assignment scope and actual service policy together. These are illustrative requirements to test; they do not assert what every Keystone role permits by default.
| Review question | Evidence to collect | Follow-up if unclear |
|---|---|---|
| Does the integration need this action? | Named operation, purpose and owner | Clarify the requirement before granting broad access |
| Is the assignment in the intended scope? | Principal, role and project/domain identifiers | Compare the assignment with the target resource |
| Is unrelated access denied? | Result of an approved negative test | Investigate policy and effective permissions |
| Who removes stale access? | Owner, expiry or review action | Assign responsibility for the lifecycle |
The output should support an administrative decision. A list of role names without scope, purpose or ownership cannot establish least privilege.
Review access across the account lifecycle
Account creation is only the beginning. Record what happens when a person changes responsibilities, a temporary assignment expires or an integration is retired. Review old tokens, credentials and service dependencies under the system’s supported lifecycle controls.
A practical review output can be simple: assignment, reason, owner, review date and agreed next action. It should help the administrator resolve exceptions rather than produce a list that nobody owns.
Keep an audit trail without leaking secrets
Log the actor, target, operation, time and outcome where the implementation supports it. A raw token or password is not useful audit evidence. Decide who can access logs and how an investigation can correlate events across the application and identity service.
A UI should show enough context to prevent an accidental assignment to the wrong project. Server-side validation and service policy must still enforce the decision. My IDMUI application article explains that separation.
Identity does not replace network security
The phrase identity is the new perimeter is a useful reminder, but it should not imply that routing, segmentation, endpoint controls and application security stop mattering. An attacker can exploit weaknesses across several layers.
For a broader design discussion, read Zero Trust in enterprise networks. For a Flask/API project involving identity operations, use the engineering support inquiry and include the intended actions, scopes and current implementation. This portfolio demonstrates lab and application work, not an independent compliance certification of an IAM deployment.