
IDMUI is my Python Flask interface for OpenStack Keystone administration. It brings identity operations into a workflow where an operator can review a project, user or role assignment and see the result of an API request.
OpenStack already has web interfaces, including Horizon. The motivation for this project is a focused custom workflow and an integration learning exercise, not that OpenStack lacks a dashboard. The related case study and repository document the implementation; the recommendations below describe what to review before production use.
Define the identity operation and its scope
Keystone concepts include users, groups, projects, domains, roles and tokens. A role assignment has meaning in a scope. An operator must understand which project or domain an action affects before approving it.
A useful interface displays the target clearly and handles stale selections. If a user opens a page, then their access changes, a hidden button is not sufficient protection. Server-side authorization and the underlying Keystone policy must still control the operation.
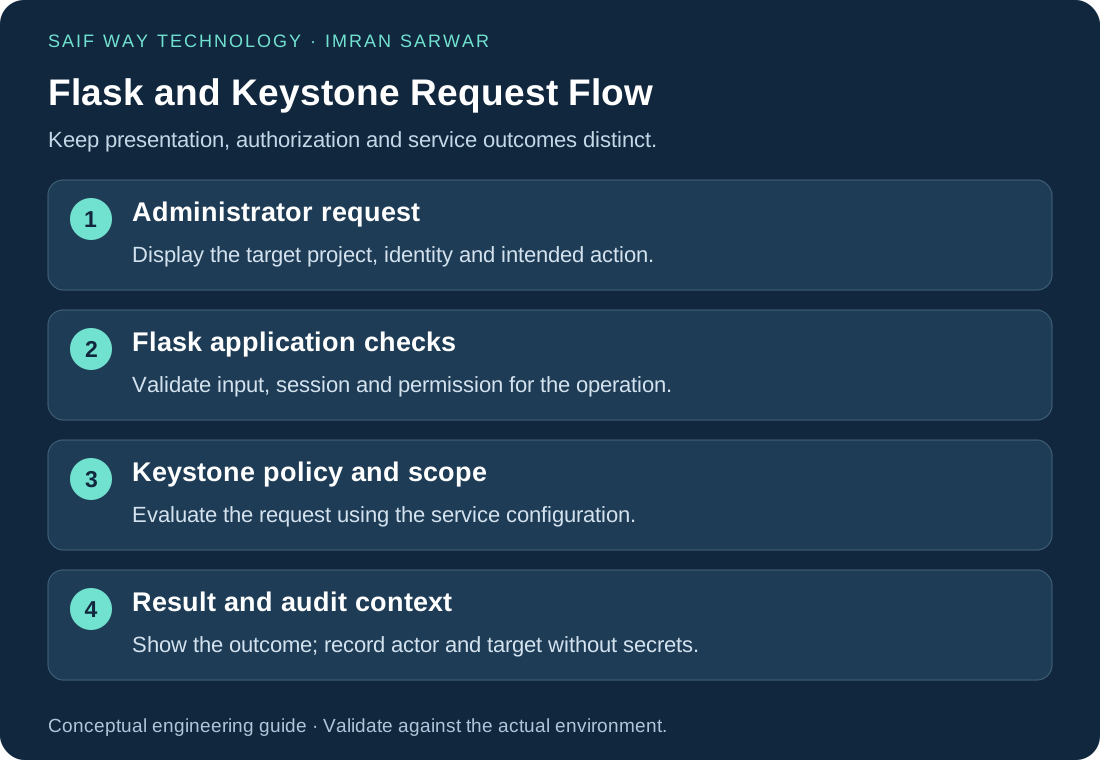
Separate identity requests, authorization and execution
The browser presents inputs and results. Flask validates the request, manages application state and calls the appropriate service. Keystone authenticates and applies its configured policy to identity operations.
Keep service credentials and tokens away from browser-readable output and source code. Decide how a session expires, what happens when a token is invalid and how a user signs out. Flask’s security guidance is a useful implementation reference for application-specific checks.
The project also explores operational service actions through SSH. Those actions have a different risk and authorization boundary from listing identity records. They should not inherit broad server access simply because a user can sign into a dashboard.
Test role assignments and API failures
For each sensitive operation, test an allowed user and a user who should be denied. Verify the target scope and examine the result when an object no longer exists, a token expires or the service is unreachable.
Return useful feedback without exposing credentials, tokens or full internal traces. Distinguish an authentication problem from an authorization denial and a transport failure. An ambiguous error can lead an operator to retry a destructive action unnecessarily.
Design a dashboard an administrator can trust
Use explicit action labels and confirmations for destructive requests. Show the selected project or domain, the current state and the result returned by the service. Record enough audit context to investigate an operation while avoiding sensitive payloads.
A custom UI should make the operation clearer, not hide important policy details. Check the Keystone role and scope documentation for the release being used; defaults and policy behavior are version-dependent.
Review the identity-dashboard implementation and integration scope
The IDMUI repository and project case study replace the earlier placeholder source link. For a similar Flask infrastructure dashboard, bring the API documentation, identity model, workflow and expected output to a remote engineering inquiry.
A working lab application is a useful starting point. Production readiness also depends on deployment configuration, permissions, testing, maintenance and the client’s access requirements.