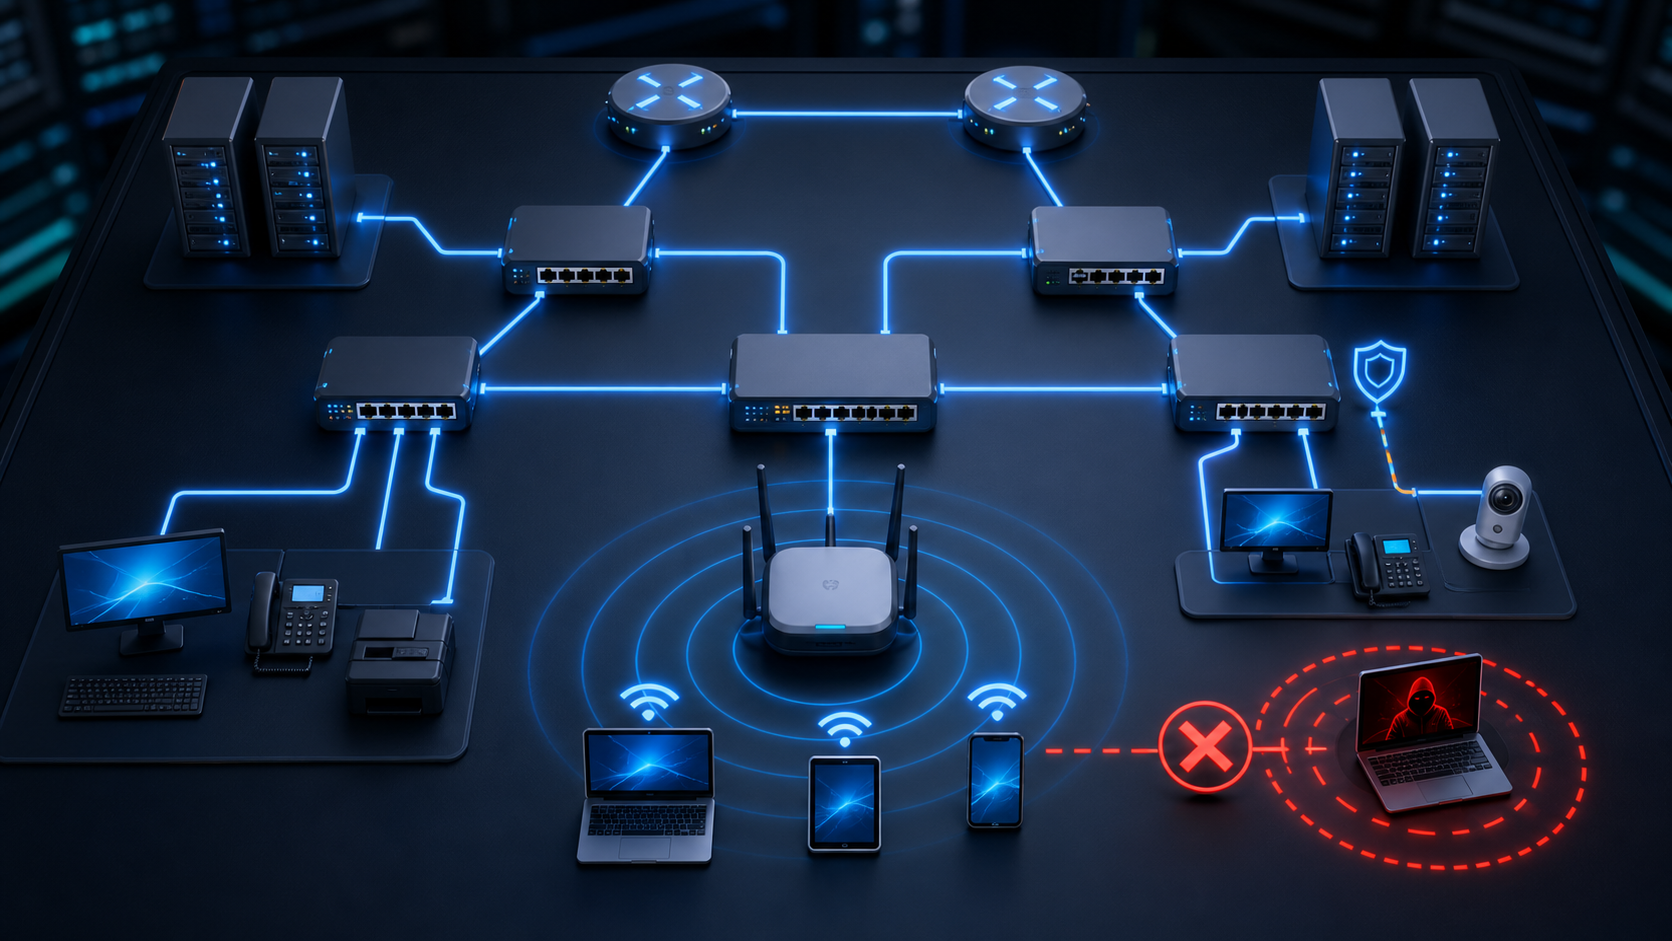
A multi-router LAN lab is useful because a failed connection can have several causes: an address or gateway error, a missing route, wireless association or a port-security policy. Fixing the wrong layer can make the topology more confusing.
My Cisco Packet Tracer project combines three routers, three switches, endpoints and wireless access. This walkthrough focuses on diagnosing the access behavior and explaining the result rather than treating a successful ping as complete security validation.
Establish LAN connectivity before applying port security
Record the subnet and default gateway of each endpoint. Confirm the local link, the gateway and the route to the destination, including the return route. The project uses RIP for the simulation; that is a lab choice, not a recommendation for every enterprise network.
Test one wired endpoint first. Then introduce the wireless path and compare the behavior. Keeping a known-working case makes it easier to decide whether a later failure comes from routing, wireless configuration or port security.
Understand the switch port and MAC learning
Port security limits the source MAC addresses allowed on a supported switch port. The maximum count and violation behavior must match the intended topology. Check the device and software documentation before assuming a command is supported.
A wireless router or access point can present different upstream behavior depending on bridging, routing and the simulator’s model. Inspect the switch MAC table instead of assuming that one cable always means one source MAC.
How do protect, restrict and shutdown violation modes differ?
The common Cisco violation modes differ in what they report and whether they disable the port. Protect and restrict can drop violating traffic; restrict adds violation reporting behavior on supported platforms. Shutdown can place the port into an error-disabled state. Confirm the exact behavior for your model in Cisco’s port-security guide.
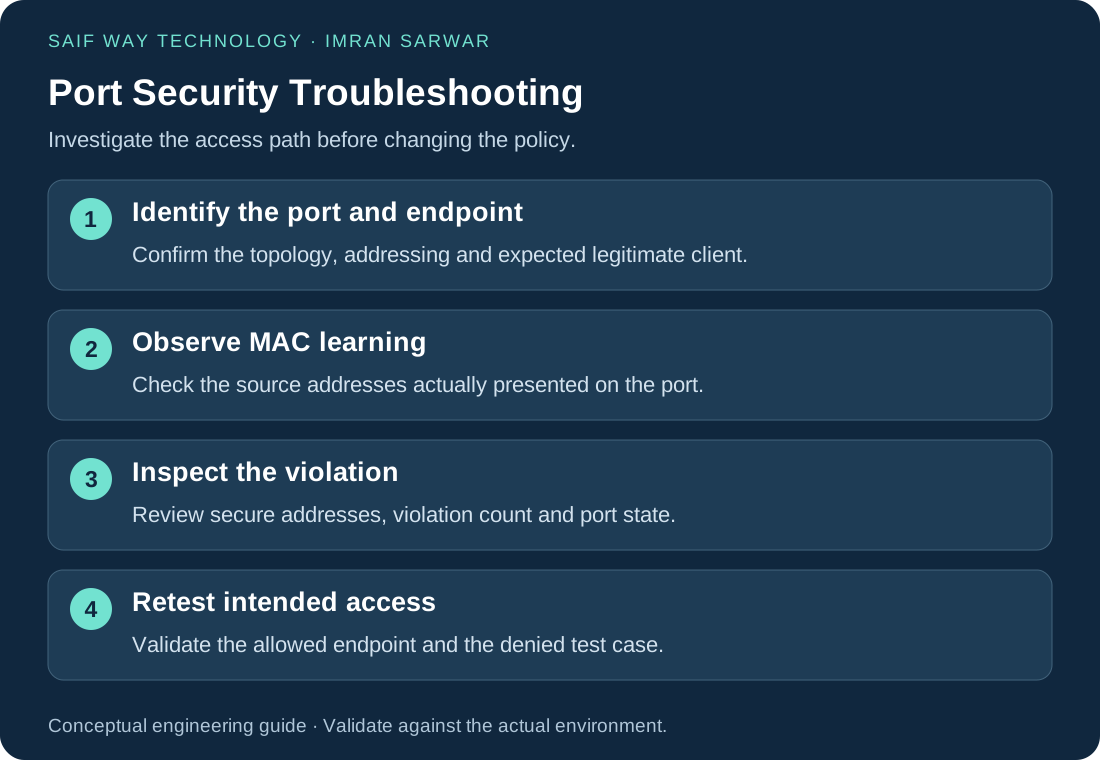
For this lab, inspect the secure address list, violation count and port status before changing the maximum. Raising the limit simply to restore access can weaken the intended test.
Validate legitimate and unauthorized access
- Record which endpoint is intended to work and why.
- Check its address, gateway and wireless configuration.
- Observe the MAC address learned on the upstream switch port.
- Introduce the second test endpoint and inspect violation behavior.
- Retest the legitimate endpoint after the restriction.
- Explain whether the result came from port security, wireless settings or routing.
MAC filtering alone is not strong identity authentication; addresses can be imitated. Keep the exercise’s learning goal separate from a production access-control design.
Review the port-security lab evidence
The video demonstration, project repository and project report provide the original context. Simulator device features vary, so describe the actual model and settings used rather than making a blanket claim about every Packet Tracer access point.
For a live connectivity issue, use remote network infrastructure support. For help understanding or documenting a student lab, use the student project help desk.